Phase 2 HIPAA Compliance Audits to Target Behavioral Health Specialists



Earlier in 2016, the Department of Health and Human Services (HHS) Office for Civil Rights (OCR) released new guidance to support their recently implemented Phase 2 HIPAA Compliance Audits.
OCR has designed these Phase 2 audits to target a broad selection of covered entities and business associates from around the country to reflect the state of HIPAA compliance across the healthcare industry. And according to HHS, that means that behavioral health specialists will be chosen as well.
For healthcare professionals who’ve been contacted, the first step is to compile a list of business associates along with appropriate contact information. OCR has posted a template on their site for selected auditees to base their own lists off of. If you’ve received an email from OCR, you should respond promptly with the information they’ve requested. In its official announcement, OCR stated that it would use publicly accessible records to compile any data they don’t receive within 10 days, so simply ignoring the issue won’t make you any less likely to be audited.
However, just because behavioral health specialists face the same regulatory requirements as other players in the healthcare field, that doesn’t mean that they face the same day-to-day challenges when it comes to managing their HIPAA compliance.
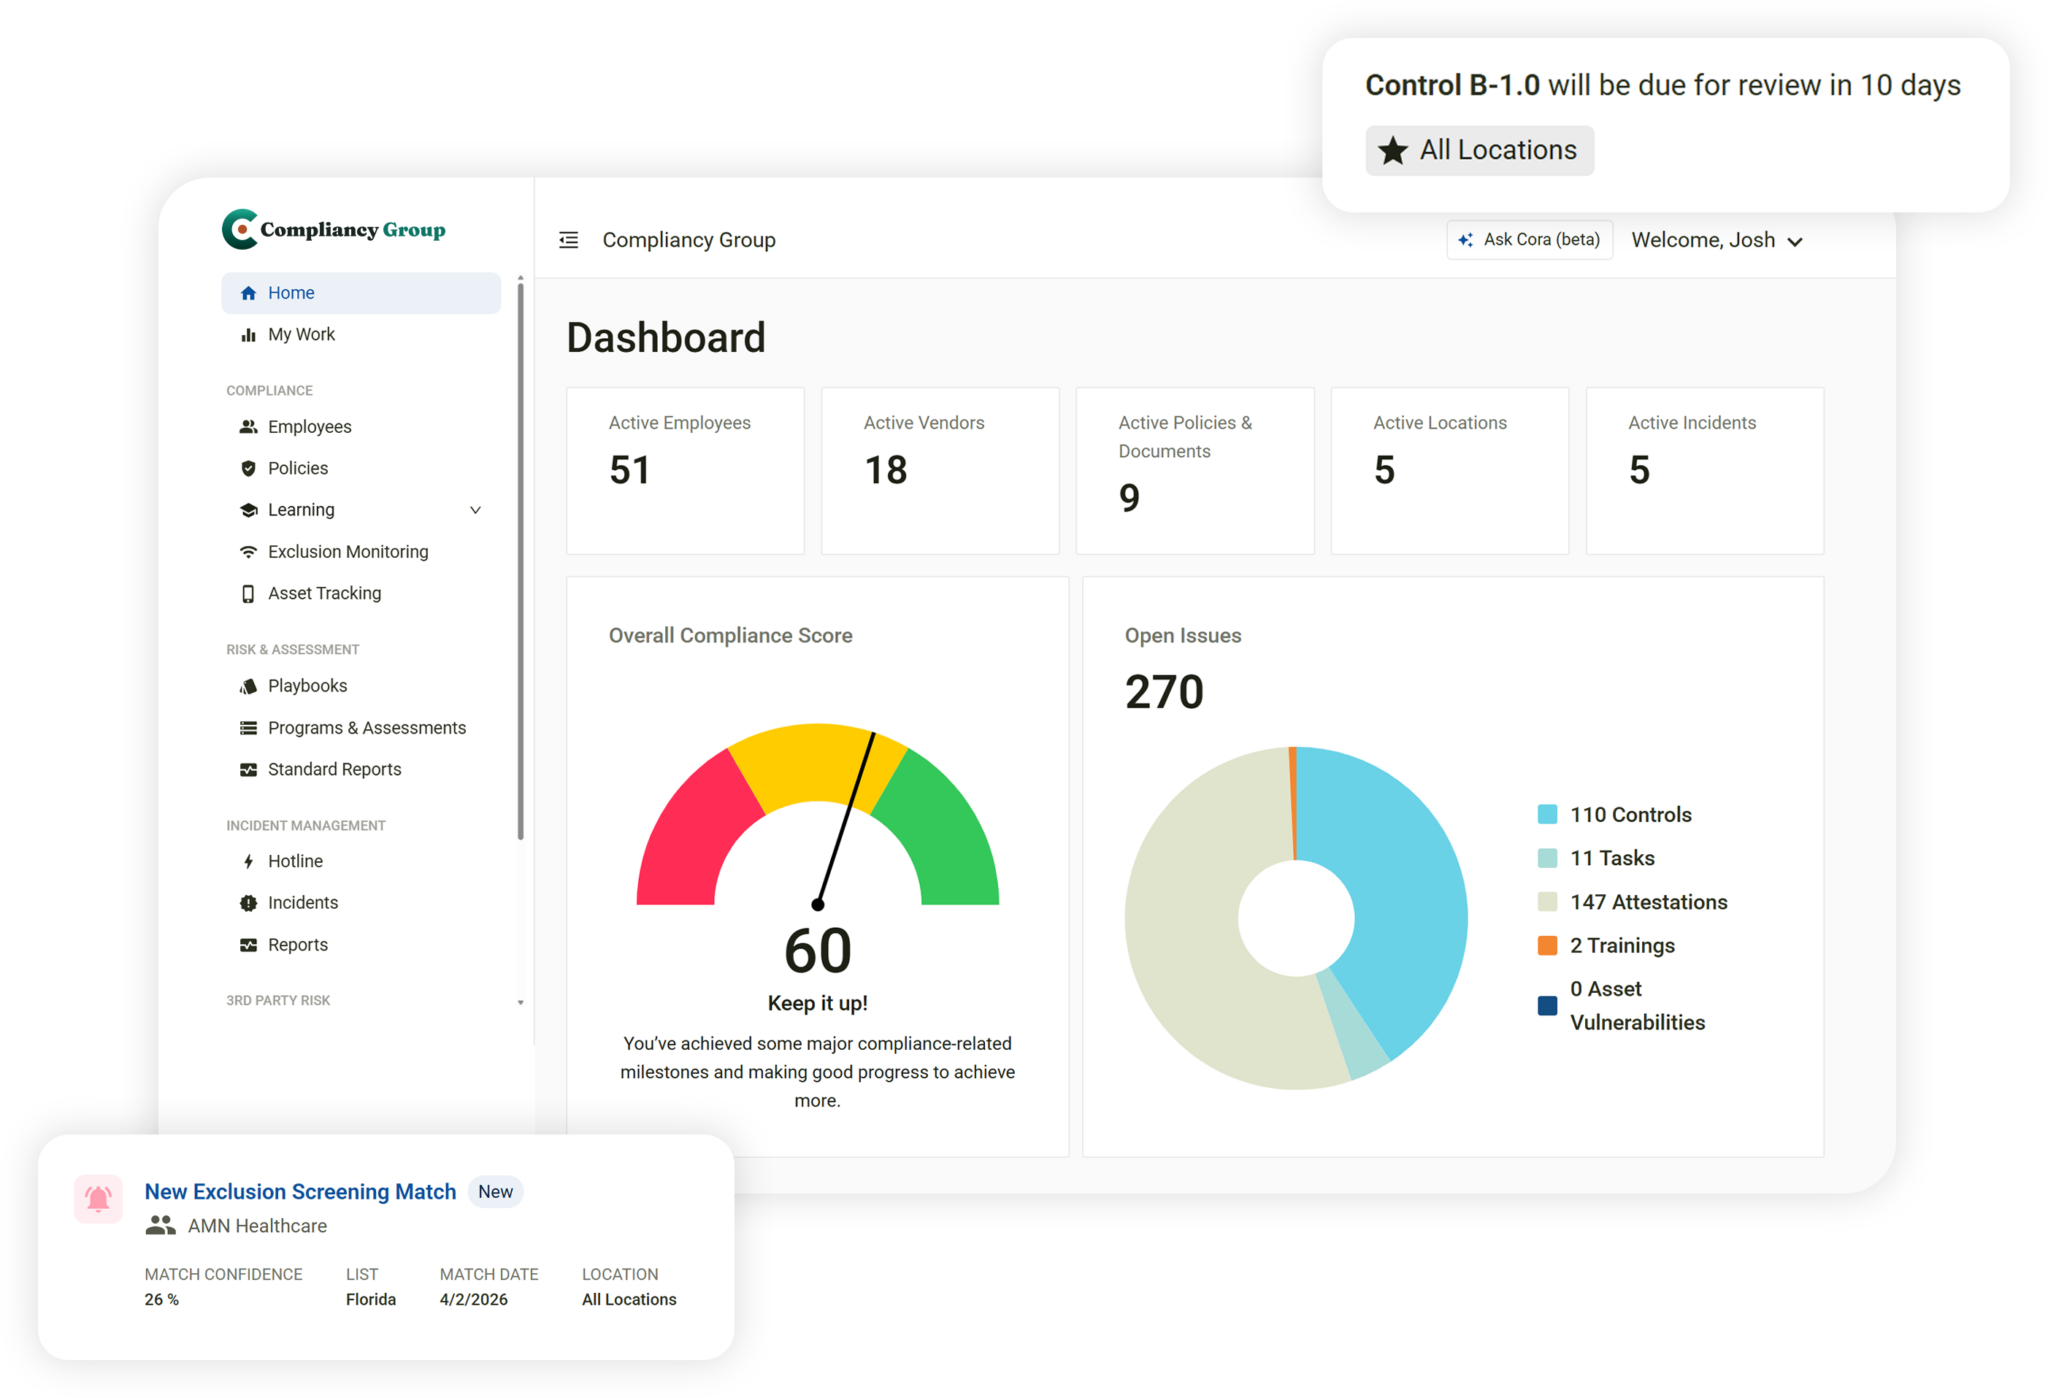
HIPAA regulation requires strict adherence to privacy and security standards throughout your behavioral health practice. You must ensure that you have addressed:
- Self-audits
- Remediation Plans
- Policies and Procedures
- Employee Training and Attestation
- Document and Version Control
- Business Associate Management
- Incident Management
With Phase 2 notifications already beginning to reach auditees, it’s more important now than ever to make sure that your practice is doing all that it can to prepare. Citing examples from previous OCR investigations, along with data gathered from across the healthcare industry, Compliancy Group provides a series of free educational webinars for behavioral health professionals. These webinars give viewers a thorough understanding of the odds they have at being audited and the steps they can take to keep OCR from knocking on their door.